Regulatory Compliance Monitoring: A 2026 Guide for Teams
Updated September 29, 2026
Editorial disclosure: This article is written by the Visualping marketing team. Visualping is one of the tools covered below, and we benefit if you sign up. We've tried to keep the buyer-education sections honest and name alternatives where relevant. The "When automated monitoring isn't enough" section is the one to read if you're comparing tools.
It's Monday morning. Your compliance officer at a mid-market bank opens her laptop and finds the CFPB pushed updated UDAAP enforcement guidance the previous Friday at 4:47pm. Her team missed it because the agency's email digest hadn't gone out yet. By the time she flags it to legal, the bank has operated under outdated assumptions for three days.
That's the gap regulatory compliance monitoring closes. UK financial-services teams can monitor the FCA website and get an alert about rule changes on the next scheduled check. For the broader picture of what compliance monitoring is across industries (not just banking), start with our complete guide. And the gap is larger than most teams realize. Across a sample of 16,208 regulator-domain pages actively monitored on Visualping (CFPB, SEC, FDA, FTC, FINRA, OCC, europa.eu, UK ICO, Canada.ca, and 10 peers), two in three (66%) changed in the 90 days to September 29, 2026, and nine in ten changed at least once in the past year. If your team is watching even 20 regulator pages manually, about eight of them move every month.
This guide covers what modern compliance teams watch, how often, how quickly different tools catch changes, and where automation stops working. If you're evaluating a tool, skip to the objection section.
The stakes: what a missed regulatory update costs
In 2024, TD Bank pleaded guilty to Bank Secrecy Act and money-laundering-conspiracy violations and paid approximately $3 billion in combined penalties across the DOJ, FinCEN, the OCC, and the Federal Reserve, including a $450 million OCC civil money penalty. In 2022, Wells Fargo was ordered by the CFPB to pay $3.7 billion ($2 billion in consumer redress plus a $1.7 billion penalty). Meta received a record €1.2 billion GDPR fine in May 2023 alone, on top of €390 million in January 2023 and more than €600 million across the preceding two years.
Fines are the visible cost. The hidden costs are larger:
- Leadership time pulled into remediation plans instead of growth
- Brand damage that shows up in deposits, customer churn, and partner audits
- Personal liability exposure for officers and directors under laws like Sarbanes-Oxley
- Insurance premium increases after a single reportable incident
The volume of regulator activity is also higher than most compliance teams estimate. In the 30 days to September 29, 2026, Visualping ran about 401,000 checks on the pages in this sample, and about 1 in 15 sent a change alert. That put roughly 26,400 regulator updates in compliance teams' inboxes in a single month.
A team that catches a rule change three days early doesn't just avoid the fine. They avoid the quarter of cleanup that follows.
Why the 2025 playbook already broke
Three tactics compliance teams leaned on before 2026 no longer hold up on their own:
Regulator email subscriptions. An agency email goes out only when the agency sends it, and a digest can hold it for up to a day or a week. GovDelivery, the platform behind FTC and Federal Register email updates, offers immediate, daily, and weekly delivery. Some sources (state AGs, international regulators) don't offer digests at all. Half of the sampled regulator monitors on Visualping check at least once a day. If your primary source is an email digest delivered the morning after, you're finding out about Friday evening changes on Monday.
Periodic manual checks. A compliance analyst with 40 URLs to review Monday morning will miss changes sooner or later. Not because they're lazy. Because manual diff-spotting on a dense policy page is a task humans fail at predictably.
GRC platforms alone. Vanta, Drata, OneTrust, and LogicGate are strong at policy management, control testing, and audit workflow. Two of them also offer curated regulatory content: OneTrust through its DataGuidance research platform, and LogicGate through integrations with CUBE, Ascent, and LexisNexis. Those feeds cover the laws and regulators their providers choose to track. A web-change monitor covers the exact regulator pages your team picks.
A modern compliance team uses all three, plus a web-change monitoring layer that checks each regulator page as often as its stakes require.
What to watch: the modern monitoring stack
Across the 16,208-page regulator sample, the five most-watched domains are the EU's europa.eu (5,159 monitors), Canada.ca (2,918), CMS (2,539), FDA (2,178), and the SEC (871). Teams rarely cover only US financial-services regulators. International, healthcare, and securities sources anchor most monitoring stacks, and healthcare teams usually add Medicare administrative contractor pages next to CMS.
Most teams start smaller than you might expect. The median business workspace in this sample watches 4 of these regulator URLs, the top quarter watch 13 or more, and the largest watches nearly 1,200. Across all government websites, the median business workspace watches 9 pages.
A practical starting inventory:
| Layer | Example sources | Check frequency |
|---|---|---|
| Federal primary regulators | CFPB, SEC, FDA, FTC, OCC rules pages | Daily |
| State regulators | Relevant state AG, DFPI, DFS, insurance commissioner pages | Daily |
| Industry bodies | FINRA, NIST, PCI SSC, ISO announcement pages | Weekly |
| Vendor ToS and DPAs | Top 10-20 vendor terms, subprocessor lists | Weekly |
| International | GDPR DPA pages, UK ICO, Canadian OPC | Weekly |
| Internal reference | Corporate policy pages, disclosure pages | Monthly |
For each source, match the frequency to the stakes. A CFPB enforcement priorities page should be checked daily. A PCI DSS press page can be weekly. The mistake most teams make is checking everything at the same cadence and drowning in noise.
How Visualping fits into a compliance workflow
Business workspaces own 59% of the live monitors in this regulator sample, spread across 407 teams.
Visualping is a web-change monitoring platform that watches any public web page on a schedule you set and sends an alert when the content changes. For compliance teams specifically, three capabilities matter:
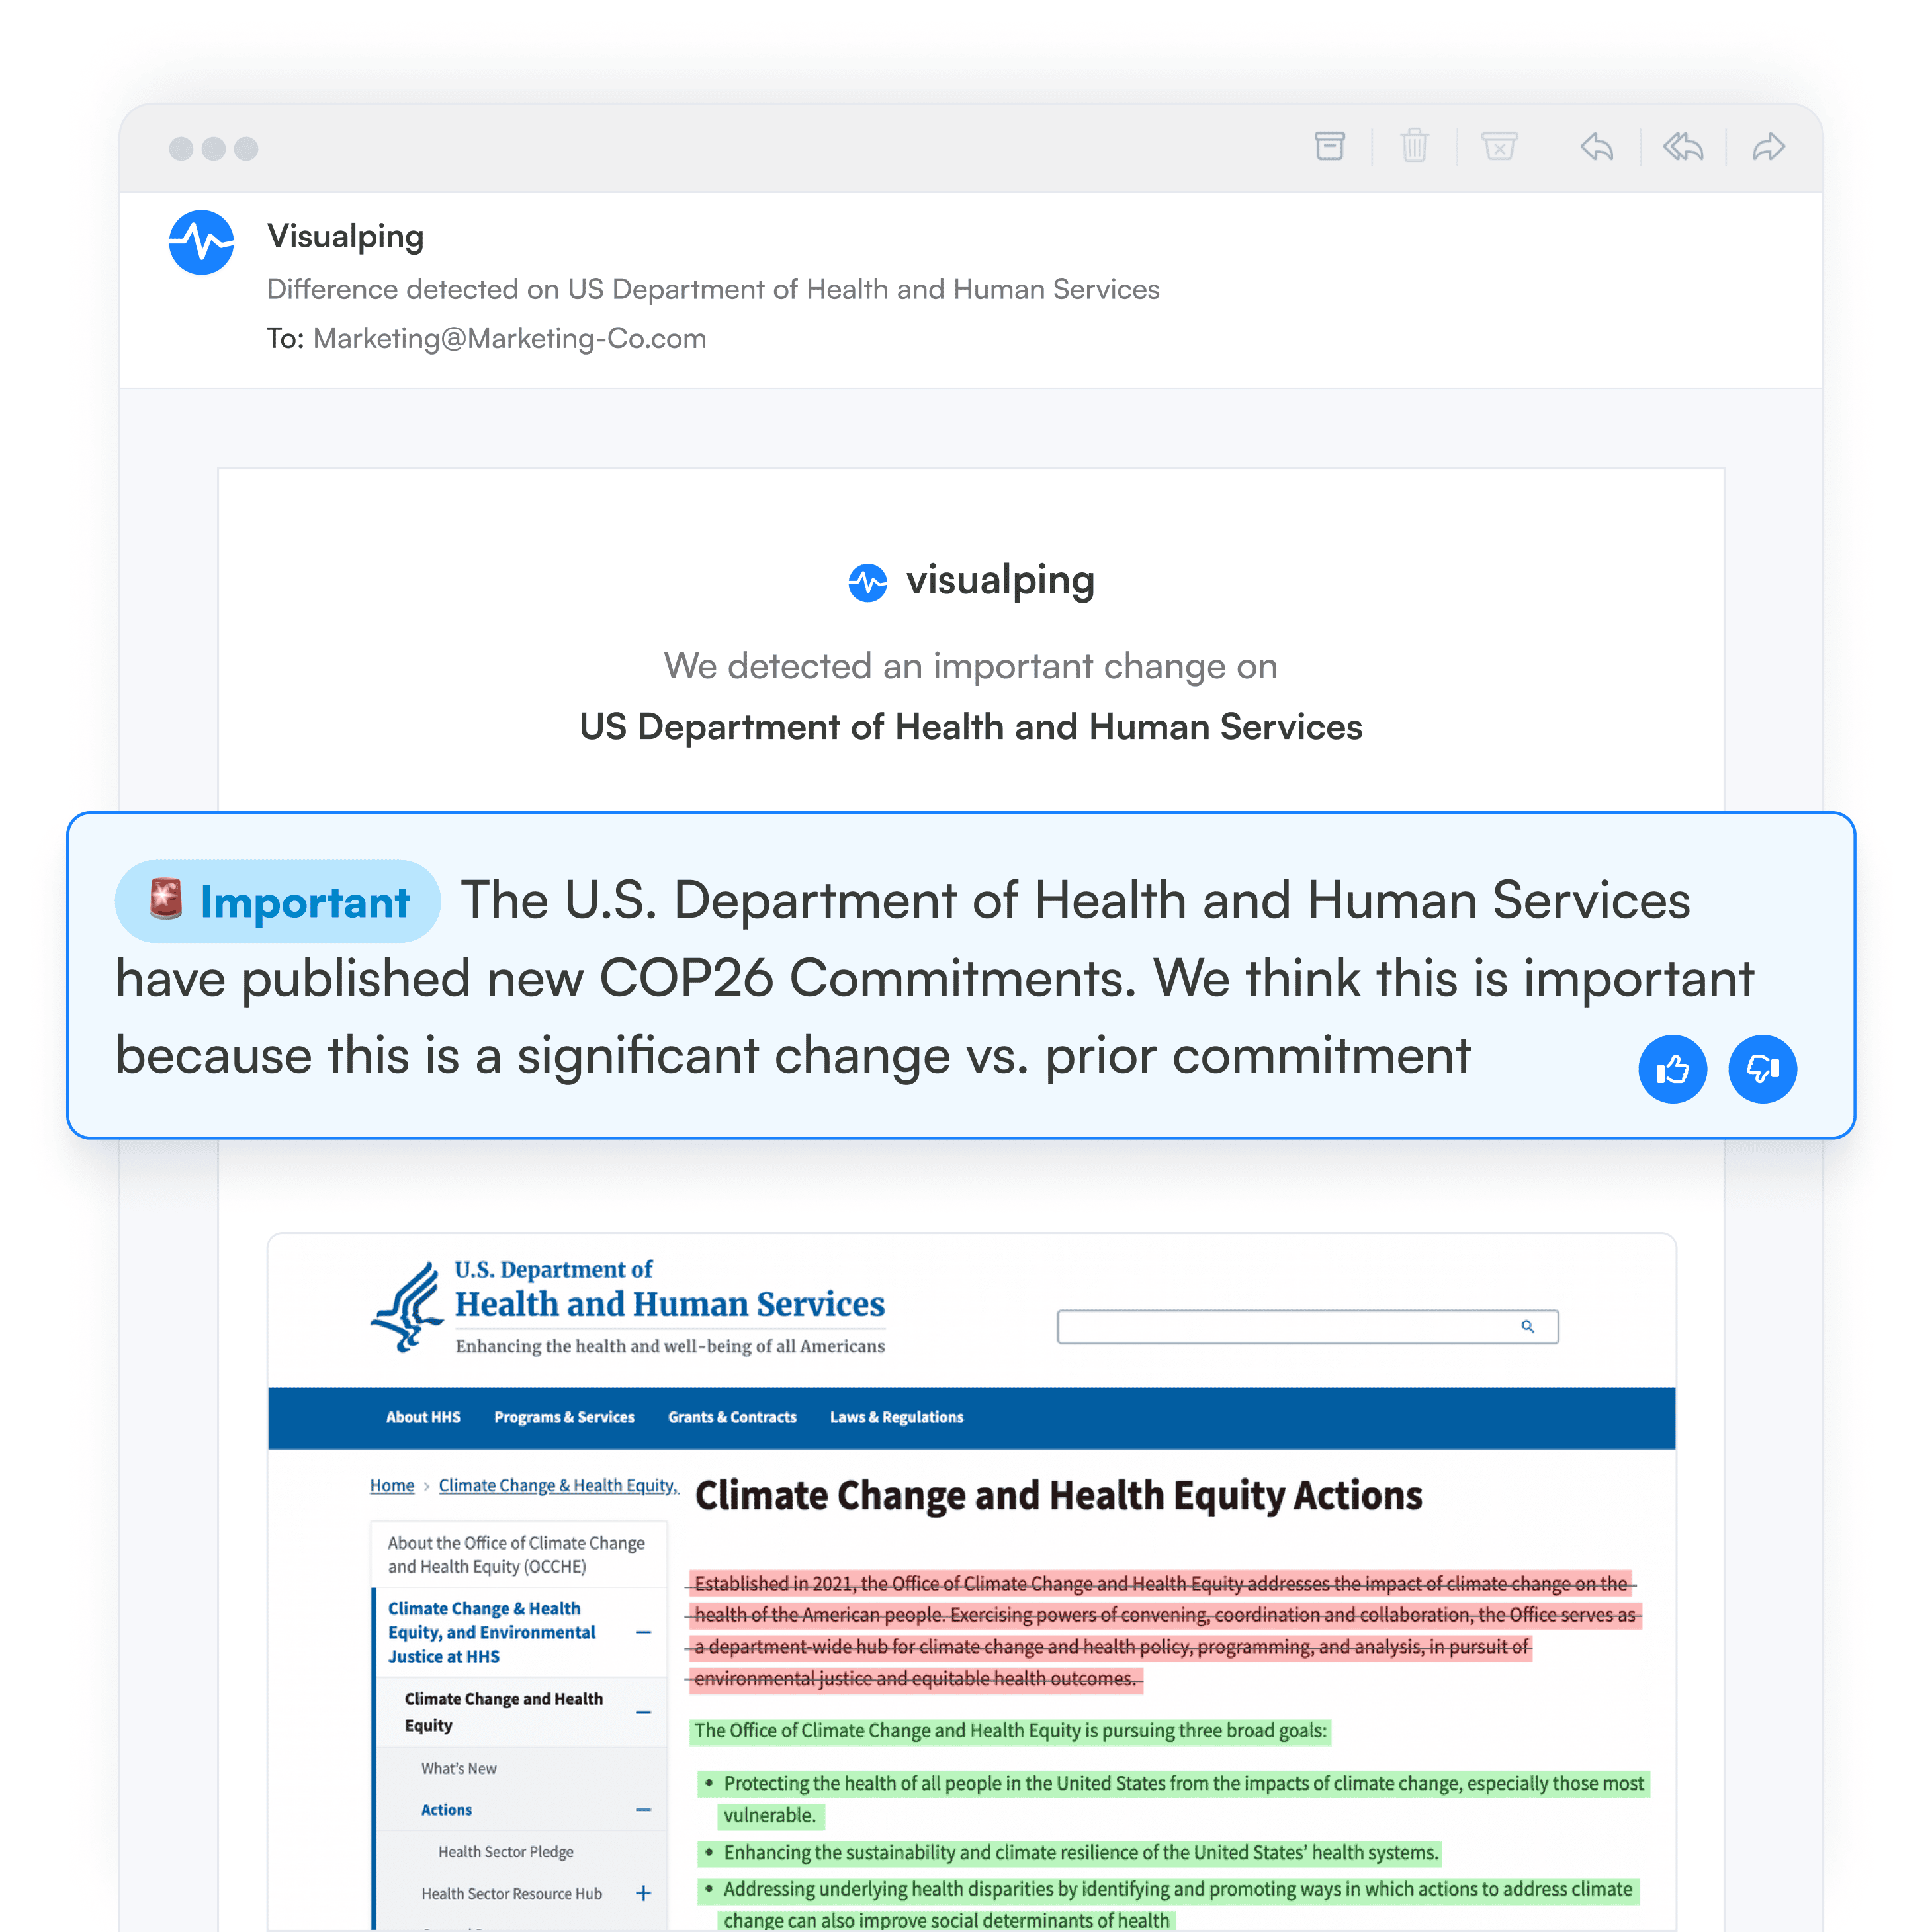
AI summaries of every change. When the CFPB changes its guidance, you get a short plain-English summary with the diff: "The CFPB withdrew 67 guidance documents, including Circular 2022-06 on overdraft fees and its 2023 policy statement on abusive practices. The withdrawals apply as of May 12, 2025." Your analyst can decide whether to escalate without reading the whole page first.
Plain-language alert conditions. New monitors default to AI Mode, where you describe the changes you care about in the "Alert me when" box. A state licensing compliance team might watch 50 DFS pages but only want alerts that mention "money transmitter" or "MLO license." Visualping uses that condition to decide which changes trigger an alert. For exact-word matching, monitors in Text mode also offer keyword alerts.
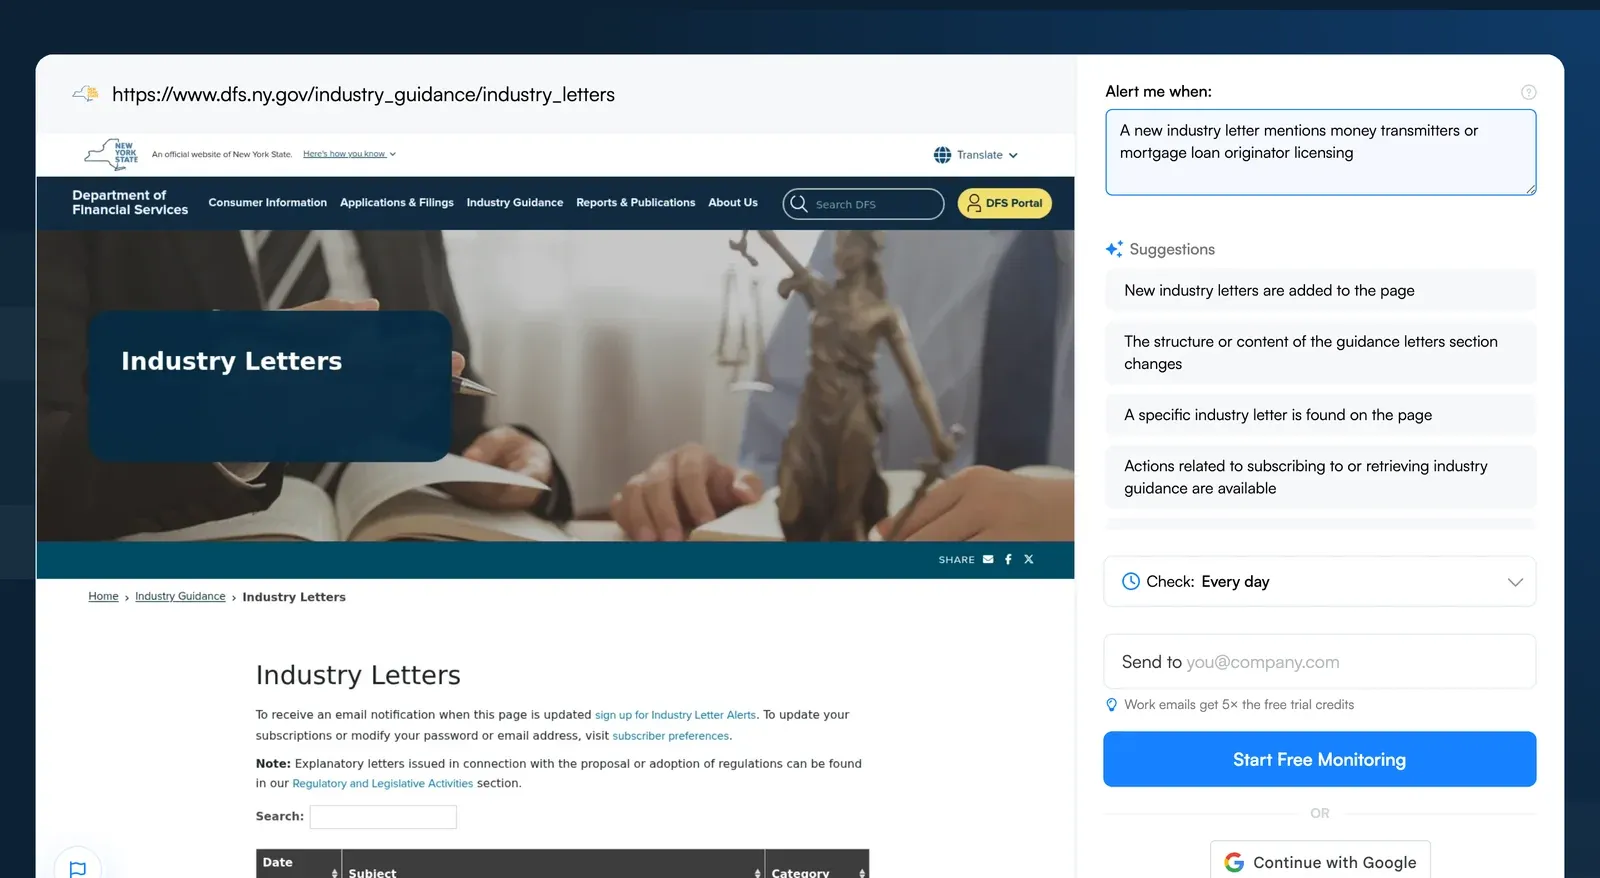 Describe the change you care about in the "Alert me when" box
Per-source frequency, as often as every 2 minutes on Personal 10k and Business plans. For a live regulatory event (FOMC day, major enforcement action), set the source to check every 2 minutes. For slower pages, set weekly. Half of the sampled regulator monitors check at least once a day, nearly all the rest check weekly or monthly, and fewer than 1 in 100 check more often than hourly. Save the fastest tiers for live events. One workspace can mix frequencies without separate accounts.
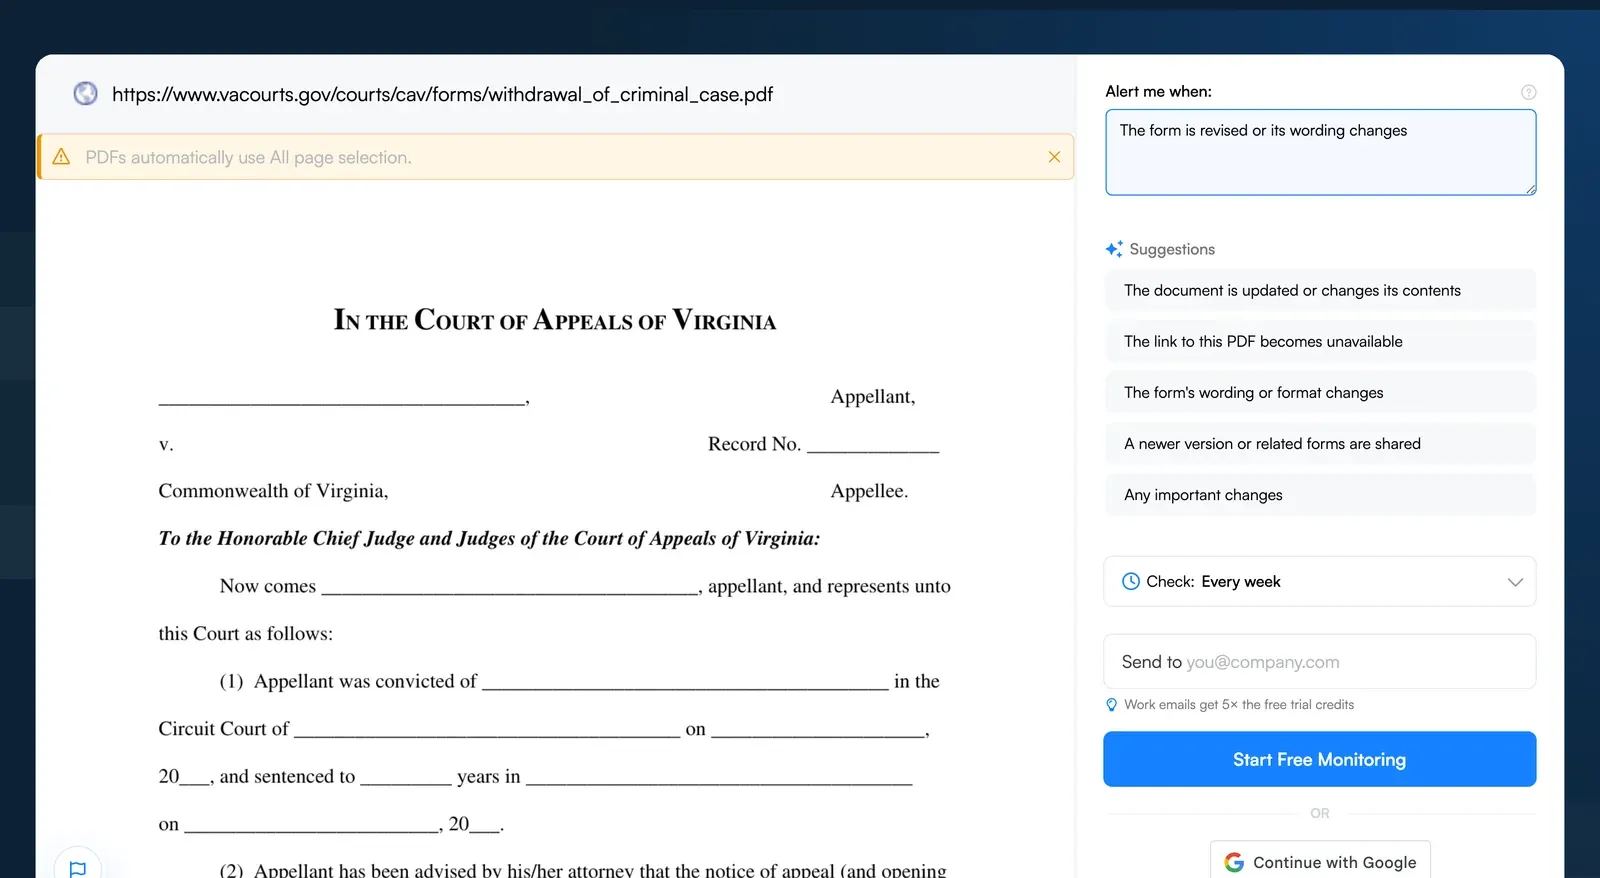 A court form PDF set to a weekly check, with the alert condition written in plain language
Visualping sends alerts to webhooks and Zapier on every plan, including Free, and to Slack and Microsoft Teams natively on Business plans, so alerts reach the right analyst without anyone checking email. For teams that prefer API-driven workflows, Visualping's webhooks post each change as structured JSON, including the added and removed text and the AI summary. The REST API is available on every plan, including Free.
For broader evaluation, compare monitoring options in this regulatory tracking software guide and this roundup of compliance monitoring platforms.
When automated monitoring isn't enough
Automated web-change detection is a detection layer, not an interpretation layer. Four scenarios require human judgment on top:
- Non-web publication. Some regulators still publish in PDF bulletins, email-only advisories, or official gazettes. Supplement web monitoring with email subscriptions and RSS feeds for these sources.
- Legal interpretation. Detecting that a rule changed is different from understanding who it applies to, when it takes effect, and what remediation looks like. Every major alert should trigger a legal review, not a compliance edit.
- Cross-jurisdiction conflicts. Federal plus state, EU plus member state, U.S. plus Canada. Automated tools catch each change. Humans reconcile which takes precedence.
- Frequency-noise tradeoff. Checking a page every 2 minutes catches changes fast but produces false positives from dynamic elements (rotating banners, A/B tests, session IDs). Tune frequency per source.
Treat automated monitoring as the top of the funnel. It tells you what changed and when. Your team, counsel, and GRC platform handle what it means and what we do.
Responding when a violation does happen
This section provides general guidance, not legal advice. Regulatory requirements and remediation expectations vary by jurisdiction and industry. Consult qualified legal counsel before acting on specific compliance obligations.
When a violation is detected, whether by your own monitoring or by a regulator's inquiry, the first 72 hours set the tone for everything that follows. Three moves in order:
- Engage counsel before responding. Every communication with the regulator should be counsel-reviewed. Unprompted disclosures have nuance that drafting teams miss.
- Preserve records, then remediate with a root-cause analysis. Put a hold on relevant documents before you change systems. The DOJ's department-wide Corporate Enforcement Policy (March 2026) counts a root-cause analysis as part of timely remediation. The same policy says the DOJ will decline to prosecute a company that voluntarily self-discloses, fully cooperates, and remediates, absent aggravating circumstances.
- Communicate proactively with stakeholders. Customers, partners, and investors all have to learn about a material compliance event from you first. Silence is read as concealment.
For the reputational management side of a compliance incident, the same principle applies: lead the narrative or the narrative leads you.
Building a compliance program that scales
A modern compliance program has four load-bearing elements:
A documented monitoring inventory. Which URLs, which regulators, which frequency, which analyst. Updated quarterly. Most programs skip this step and pay for it later when a new analyst can't figure out what's being watched.
A triage flow. When an alert fires, who reviews? Who escalates? What's the SLA? A 4-hour escalation window on federal regulatory changes is a reasonable target for a mid-market team.
Quarterly control testing. Monitor that your monitoring works. Run a known change through and verify the right people got the alert within SLA.
Cross-functional access. Compliance, legal, product, and engineering should all see the same regulatory feed. Siloed compliance teams catch changes late because they don't know which internal team owns the affected product surface.
For a deeper treatment of regulatory change management and horizon scanning, we've written stand-alone pieces that connect to this guide.
Frequently Asked Questions
What is regulatory compliance monitoring?
Regulatory compliance monitoring is the continuous tracking of laws, regulations, and industry standards to identify changes that affect an organization's obligations. It combines automated monitoring of government and regulatory websites with internal review to flag updates that require policy, training, or operational changes.
How often should compliance teams check for regulatory changes?
It depends on source criticality. Among sampled regulator monitors on Visualping, half check at least once a day and nearly all the rest check weekly or monthly. Primary federal regulators (CFPB, SEC, FDA) warrant at least a daily check. Industry bodies and vendor terms-of-service can be weekly. Low-risk reference pages can be monthly. The common mistake is one-size-fits-all frequency, which either creates noise or misses time-sensitive changes.
What is the difference between regulatory change management and regulatory intelligence?
Regulatory change management is the operational process of detecting, interpreting, and implementing specific rule changes. Regulatory intelligence is the broader strategic practice of analyzing trends, anticipating future rulings, and engaging with regulators. Mature compliance programs run both.
Which industries need regulatory compliance monitoring the most?
Financial services, healthcare, insurance, legal services, pharmaceuticals, energy, and food safety have the densest regulatory surface area. Any organization handling personal data under GDPR or CCPA, or operating across jurisdictions, also needs active regulatory tracking regardless of vertical.
Can regulatory compliance monitoring be fully automated?
Detection can. Interpretation cannot. Automated tools watch regulatory websites and notify teams when content changes, which handles the detection layer reliably. Interpretation of what a change means, who it applies to, and what action is required still requires qualified compliance and legal judgment.
Start watching your first five regulatory pages
Pick the five regulatory URLs your team would be most embarrassed to miss a change on. Paste each into Visualping. Set each one to check daily. You'll get an email the next time any of them change, with a short Visualping AI summary of what moved.
No credit card. The Free plan includes five pages and 150 checks per month, enough to check five pages about once a day. If it's useful, your team can expand from there.
Want to stay on top of non-compliance?
Sign up with Visualping to detect issues from any web page online – before your business is on the line.
Eric Do Couto
Eric Do Couto is the Head of Marketing at Visualping. He leads content strategy, growth operations, and brand positioning for website change detection.
More articles by Eric Do Couto