What Is Website Defacement? How to Detect and Monitor for It
Updated October 1, 2026
Your website is often the first impression a customer gets of your business. When hackers deface it, they take that impression hostage: your homepage becomes their billboard, and every visitor who lands there sees their message instead of yours.
This guide explains what website defacement is, shows real attacks against companies and governments, and walks through how defacement happens, what it costs, and how to detect it at the next automated check instead of days later.
What Is Website Defacement?
Website defacement is a cyberattack that changes the visible content or appearance of a webpage. Attackers swap your homepage for their own images, replace your copy with political messages or taunts, or redirect visitors to entirely different sites.
The graffiti comparison fits. Vandals tag buildings to make a statement or claim territory; hackers deface websites for the same reasons: political protest, bragging rights in hacker communities, or simply to prove they got in. Security researchers call the political variety "hacktivism," and it accounts for many of the highest-profile incidents.
The dangerous part is the delay. A defaced page keeps serving your visitors until someone notices. Sometimes the first alert is an email from a confused customer asking why your homepage is showing offensive content. By then, it is hard to know how many people saw it.
Real Website Defacement Examples
Three documented incidents show the range, from juvenile to geopolitical:
- Lenovo: In 2015, visitors to Lenovo's main website were greeted with a slideshow of bored teenagers set to "Breaking Free" from High School Musical. The attackers, a group called Lizard Squad, linked to their own Twitter account from the defaced page. The stunt was retaliation for Lenovo's Superfish adware scandal.
- Fast Company: In September 2022, attackers broke into the business publication's CMS and replaced every headline on its homepage with an obscene and racist message. Two days later, a similar message went out twice to its Apple News followers, and Fast Company took its entire website offline. The site stayed dark for eight days while the breach was investigated.
- Ukraine government websites: In January 2022, attackers targeted roughly 70 Ukrainian government sites in a single night and defaced at least 10 of them, including the Ministry of Foreign Affairs and Cabinet of Ministers, with a warning telling citizens to "be afraid and expect the worst." The defacement coincided with destructive wiper malware deployed against government networks.
The pattern across all three: the damage scaled with how long the defaced content stayed up and how the organization responded.
How Website Defacement Happens
Four entry points show up again and again:
- Compromised CMS or plugins. Outdated WordPress installs, unpatched plugins, and abandoned themes are a common route: in Sucuri's 2023 hacked-website report, 39.1% of CMS applications on infected sites were outdated at the point of infection. Attackers scan for known vulnerabilities across millions of sites at once; yours gets hit because it matched a signature in a scan that also hit ten thousand others.
- Stolen admin credentials. These leak through phishing, through credential stuffing from breached password lists, or through a former contractor's account that nobody revoked.
- Vulnerable third-party scripts. Anything loading from an external source (chat widgets, analytics tags, ad scripts) can change what your page shows without your own servers ever being breached. Web skimming crews like Magecart have used this route to hit hundreds of sites at once.
- DNS hijacking. The attacker never touches your site at all. They redirect your domain to a server they control, and visitors see their content at your address.
The third and fourth routes matter because they defeat server-side defenses. A file integrity monitor watching your own infrastructure sees nothing wrong while your visitors see a defaced page. Detection has to include what the page actually renders in a browser.
What a Defacement Costs
The visible vandalism is the cheap part. Customers who saw the defacement now wonder whether their data is safe with you, and that doubt outlives the cleanup. Google can flag or de-index compromised pages, and its help page warns that being flagged may affect your search ranking for a while. Sales stop while the site is down. Then come the recovery costs (restoring content, investigating the breach, hardening whatever broke) and, if customer data was accessible during the incident, disclosure obligations on top.
For regulated businesses, timestamped evidence of what appeared and when becomes important for insurance claims and disclosure decisions. Capture it during the incident, following the practices in our guide to screenshots as evidence.
Go deeper: Cost of Website Defacement: Key Factors and Financial Impact | PCI DSS 11.6.1: How Change Detection Supports Compliance
How to Detect Website Defacement
Manual checks fail for a simple reason: defacement happens at machine speed and gets discovered at human speed. Nobody reloads their own homepage at 3 a.m.
Some teams already automate this. Among 885 Visualping business workspaces registered with a company email domain, 112 (about 1 in 8) monitor at least one page on their own website, and those monitors run on tighter schedules: 94% check at least daily, against 80% of the same workspaces' other monitors (Visualping data, October 2026). Half of those own-site pages (49%) changed at least once in the past 30 days, so a defacement alert has to stand out from your team's routine updates.
Automated detection comes in three layers:
- Uptime and keyword monitors confirm your site responds and that expected text is present. They catch outages and crude replacements, but miss visual changes and subtle content swaps.
- File integrity monitoring watches your server's files for unauthorized changes. It catches tampered files on your server. It can miss changes stored in the database, it is blind to third-party script and DNS attacks, and it needs server access to set up.
- Visual change detection checks the rendered page the way a visitor's browser sees it, and flags changes regardless of where they originated. This layer can catch a visible defacement from any of the four attack routes above.
Here is how to set up visual detection with Visualping:
- Step 1: Go to the Visualping homepage, paste the URL of the page you want to watch (start with your homepage) into the URL field, and click Go. A preview of the page loads.
- Step 2: Describe what a defacement would look like in the Alert me when box. For example: "Unexpected text, images, or links appear on the homepage, or its layout changes."
- Step 3: Choose a check frequency in the Check menu. The Free plan checks as often as every hour, and Personal 10k and Business plans check as often as every 2 minutes, which keeps your exposure window to minutes rather than hours.
- Step 4: Enter the email address for alerts in Send to and click Start Free Monitoring, then create your account and confirm your email.
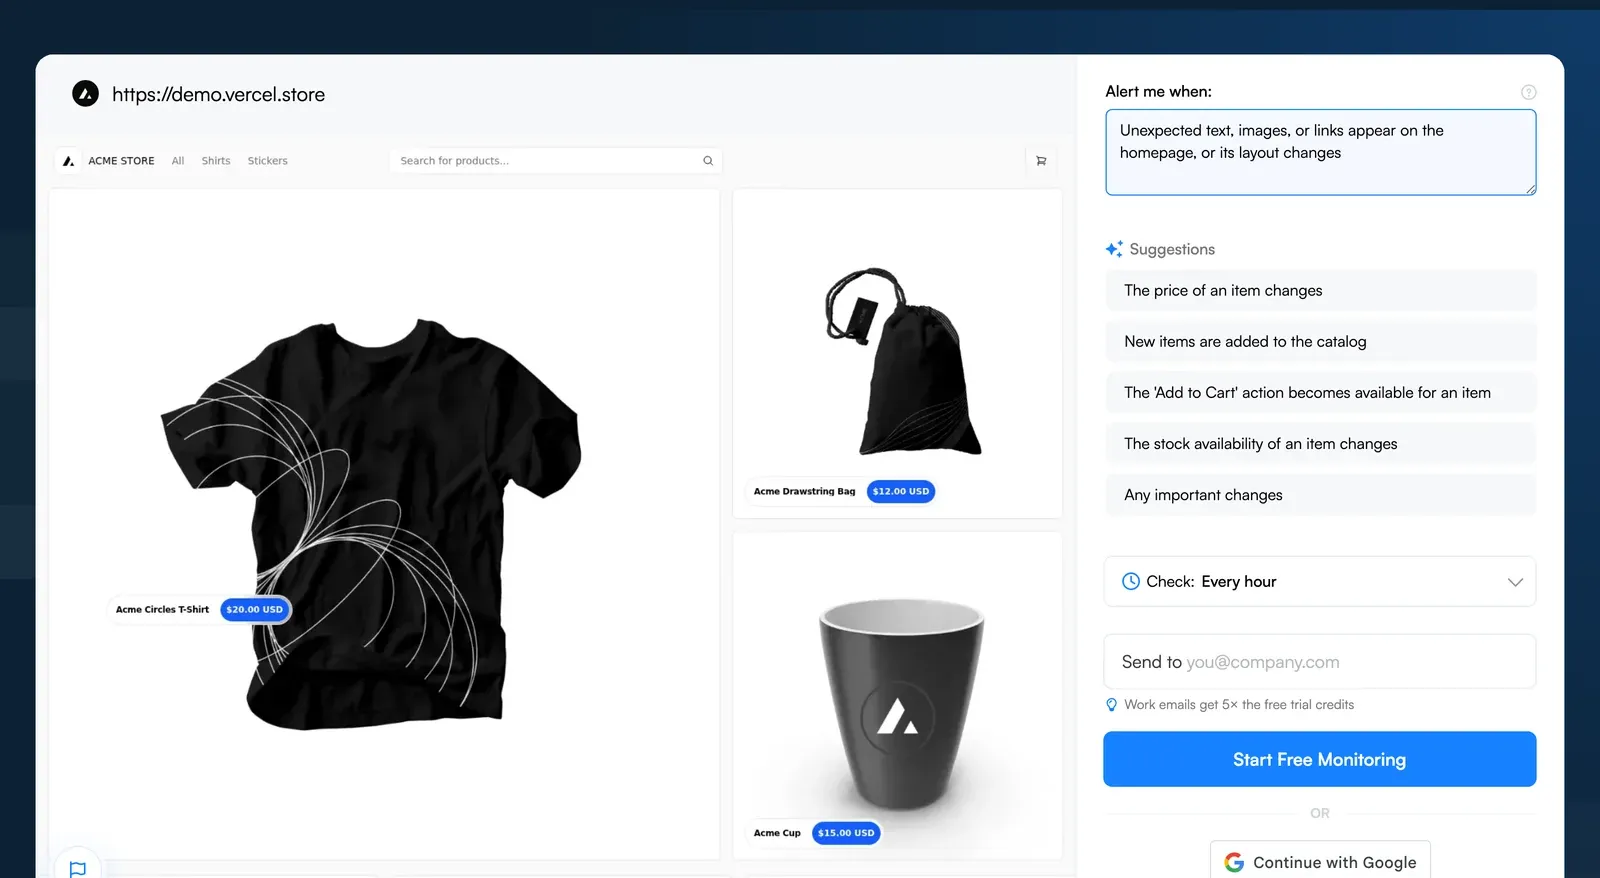 Describe what a defacement would look like in the "Alert me when" box
New monitors use AI Mode by default, which watches text, visual and page-element changes together, so there is no compare type to choose.
The same AI-prompt setup works for any page you need to watch; our guide to monitoring a web page with AI walks through prompt writing in more depth.
When a change matches your "Alert me when" condition, Visualping AI tags it Important and sends an alert with a plain-language summary of what changed. By default, Visualping records other changes in the monitor's history without sending an alert. That means a redesigned footer at 3 a.m. stays quiet, while "your homepage now shows a political manifesto" reaches you as the emergency it is. (That filtering is deliberate; we wrote up how Visualping cuts false positives if you want the mechanics.)
If you are evaluating dedicated tooling for your security stack, our website defacement monitoring page covers the commercial side: pricing, the 14-day free trial, and setup help for teams.
What to Do if Your Site Gets Defaced
Respond quickly, in this order:
- Document first. Take screenshots of the defaced pages before touching anything. You will need them for the investigation, for your insurer, and possibly for law enforcement.
- Take the site offline if the defacement is offensive or the attacker may still have access. A maintenance page beats a manifesto.
- Contact your hosting provider. They can check for server-level compromise and may have logs you can't see.
- Restore from a clean backup. Pick one dated before the intrusion itself, since the attacker may have had access before the visible defacement appeared.
- Find the entry point before going back online. Restoring the site without patching the vulnerability invites a repeat. In one study of over 9 million defacement records, attackers hit some sites again and again for up to seven years.
Frequently Asked Questions About Website Defacement
Q: Is website defacement illegal?
A: Yes. In the US it falls under the Computer Fraud and Abuse Act, and most countries have equivalent laws against unauthorized access to computer systems. Prosecution is another matter: many defacement crews operate across borders, which is why prevention and fast detection carry more practical weight than legal recourse.
Q: How quickly can a defacement be detected?
A: With automated visual monitoring, within one check cycle: as little as 2 minutes on Visualping's Personal 10k and Business plans, or an hour on the Free plan. Without monitoring, the average is however long it takes a customer to email you. The gap between those two numbers is the reputational damage.
Q: Does defacement mean my customer data was stolen?
A: Not necessarily. Many defacements only touch the public-facing page, and data theft is a different attack with different goals. But a defacement proves someone gained control of what your visitors see, so treat it as a full incident: investigate what else the attacker could reach, and involve your hosting provider or a security professional before assuming the damage was cosmetic.
Protect your site from defacement today
Get instant alerts when unauthorized changes occur on your website with Visualping's powerful monitoring tools. Start today!
Eric Do Couto
Eric Do Couto is the Head of Marketing at Visualping. He leads content strategy, growth operations, and brand positioning for website change detection.
More articles by Eric Do Couto